
Exciting new series on “Voice, Body and Movement for Lawyers – How to connect with the jury and find Justice Through Dramatic Technique!”
Click here to find out more
Part 3 of this 4 Part series. Building on Parts 1 and 2, Part 3 of this series represents a deeper dive into the nuances of the SEC Cyber Proposal, EU NIS 2, EU DORA, and ONCD Strategy. Once the foundation has been laid, the presenters will explain how to integrate these items into assessing cybersecurity risk.
Key Objectives:
• Explain SEC Cyber Proposal, EU NIS 2, EU DORA, and ONCD Strategy.
• Appreciate how the legal items should be integrated into assessing cybersecurity risk.
• The potential fiduciary impact on executives and boards.
Confidentiality Agreements (also called NDAs) are too often treated as routine. So routine, th...
Conducting an internal investigation that is incisive, effective and legally compliant is tough enou...
Join us for this presentation to learn about the U.S. Court of Appeals for the Federal Circuit litig...
2026 was a very important year when it comes to federal procurement developments, Artificial Intelli...
This program examines the scope, jurisdiction, and exceptions to the Federal Arbitration Act (FAA), ...
Unrecorded time, vague entries, and end-of-month write-offs cost firms significant revenue. This pra...
AI tools and workplace silence create the same problem for legal teams: the safeguards in place, inc...
Every tax lawyer, business lawyer, estate planner, and white-collar practitioner eventually meets a ...
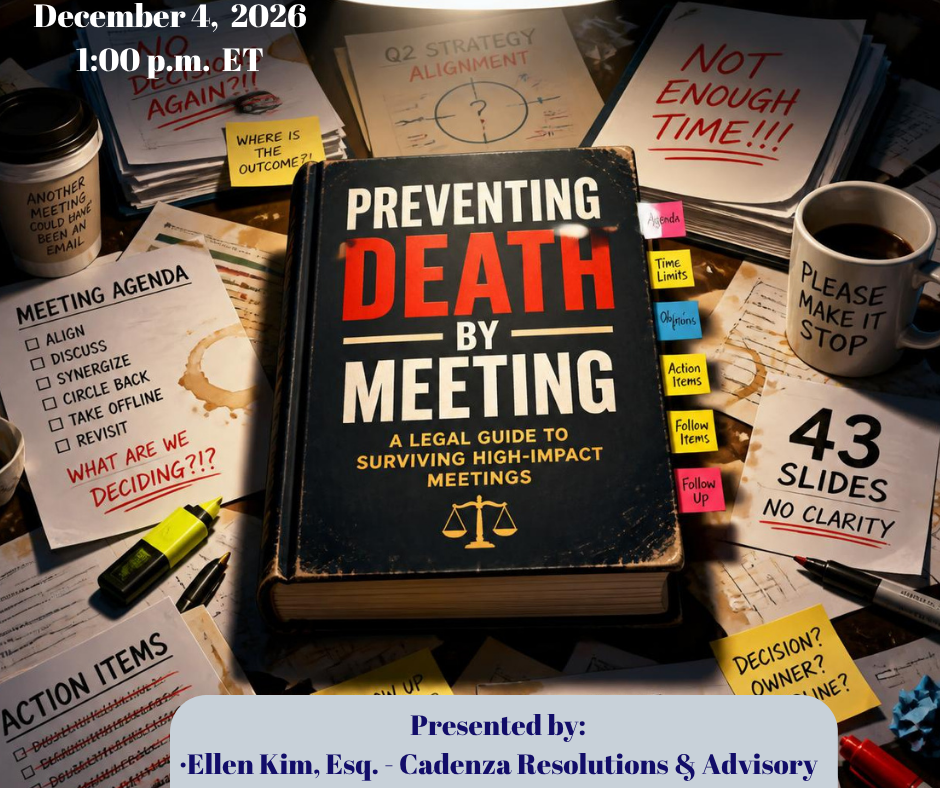
Lawyers lose hundreds of billable and operational hours every year to poorly managed meetings. Unfoc...
The legal industry is in the middle of the largest generational transfer of law firm ownership in it...