
Exciting new series on “Voice, Body and Movement for Lawyers – How to connect with the jury and find Justice Through Dramatic Technique!”
Click here to find out more
The SEC has been increasingly active in targeting cybersecurity practices, issuing new rules governing disclosures of cybersecurity measures and risks, management and board oversight of such risks, and reporting of significant cybersecurity incidents.
This program will provide an overview of the new rule governing public companies, with a specific focus on the requirement report material cybersecurity incidents within four business days, and a recent enforcement action putting Chief Information Security Officers directly in the SEC’s enforcement cross-hairs. Attendees will leave with a practical understanding of what’s required to comply with the new rule and key takeaways for companies to consider for compliance.
As the largest purchaser of goods and services in the world, the United States Government requires f...
Class action waivers in arbitration agreements remain enforceable, but a decade of U.S. Supreme Cour...
This course on trade secrets litigation provides real-world best practices through all key stages of...
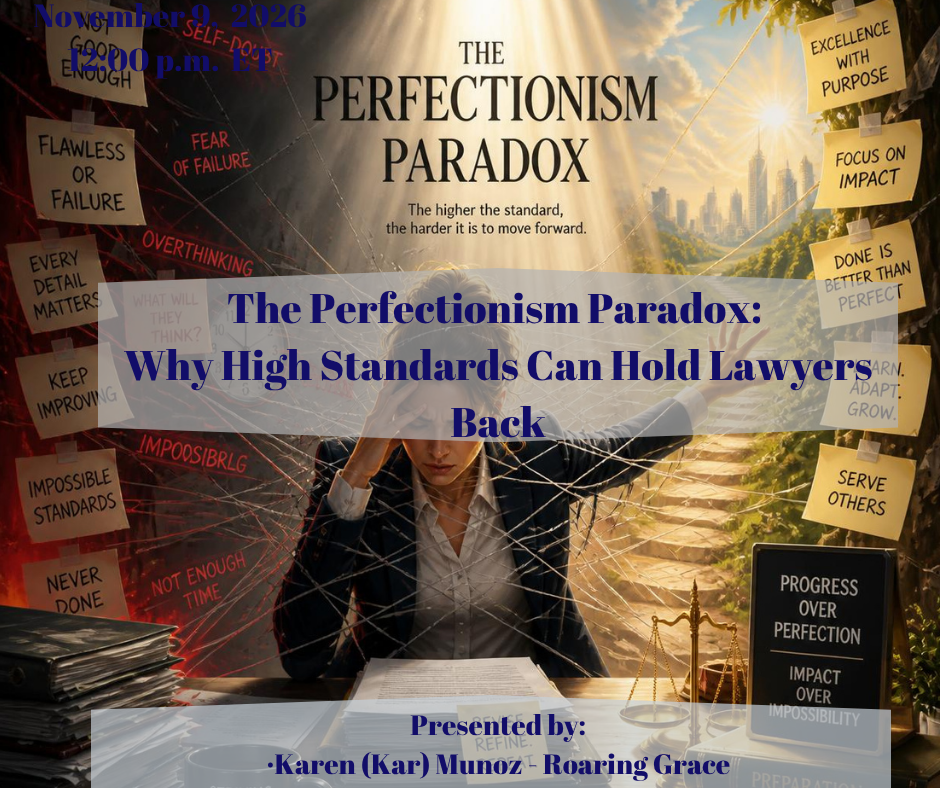
Perfectionism is often rewarded in the legal profession. It drives attention to detail, thorough pre...
Lawyers lose hundreds of billable and operational hours every year to poorly managed meetings. Unfoc...
The practice of law places legal professionals under extraordinary and often chronic stress, making ...
Turn decades of client relationships into lasting equity. This practical CLE shows attorneys how to ...
Data privacy remains one of the most rapid areas of growth in the class action space. Plaintiffs con...
This program will discuss how to design and implement legally sound diversity, equity, and inclusion...
Class action litigation continues to expand in both number of filings and monetary exposure, with se...